The First Signs of AI-Driven Cyberattacks (and How Defense Changes)
AI is making phishing, voice scams, and recon cheaper and more convincing. The first wave is already here, and it favors attackers.
- 11 claims
- 11 match a source
- 0 need one
- 0 unreachable
11 of 11 claims match a source
Claim by claim: what the check found
| Claim | Finding |
|---|---|
| AI is likely to increase the scale and sophistication of cyberattacks in the near term | Matches a source |
| The first wave is existing attacks made cheaper and harder to spot, not new kinds of attack | Matches a source |
| AI lowers the cost of reconnaissance and tailored social engineering | Matches a source |
| Sophisticated AI-enabled operations still require expertise | Matches a source |
| Phishing and social engineering are prevalent causes of breaches | Matches a source |
| A short audio sample can be enough to generate a convincing voice clone | Matches a source |
| Security guidance increasingly treats voice and video as unreliable signals | Matches a source |
| Polymorphic malware existed before AI | Matches a source |
| The FBI's IC3 publishes Internet Crime Reports covering fraud and business email compromise | Matches a source |
| CISA phishing guidance covers controls and defensive posture | Matches a source |
| NIST publishes the AI Risk Management Framework (AI RMF 1.0) | Matches a source |

The first signs of AI-driven cyberattacks
For years, cybersecurity experts warned about AI-powered attacks: instant vulnerability discovery, undetectable impersonation, and malware that adapts on the fly. Those apocalyptic versions are not the daily reality for most organizations yet. What is here is more important for most people and most firms. AI is making existing attacks cheaper, cleaner, and harder to spot.
The first wave is not a Hollywood scene. It is a thousand small escalations that shift advantage toward attackers. Better writing, better targeting, better imitation, and faster iteration. Each change is incremental. Together, they change the baseline.
1) Phishing that passes human scrutiny
Old phishing often failed because it was sloppy. The email sounded wrong. The grammar was off. The urgency was too obvious. The greeting was generic. Humans could catch it, and training programs had a real return.
AI phishing changes the failure mode. The message can be fluent and context-aware. It can resemble the way a real colleague writes. It can use internal language like “quick sync,” “circling back,” or a project name pulled from a public slide deck or a job posting. It can do this at scale. The attacker does not need to spend an hour crafting one perfect email. They can generate dozens of plausible variants, test which ones get clicks, and iterate.
When phishing stops looking like phishing, training alone does not hold. Training still matters, but it has diminishing returns once the signal is not obvious. Defense has to shift toward controls that assume some messages will persuade.
2) Voice cloning breaks “I recognize their voice”
Voice used to function as informal authentication. It was never perfect, but it was real. If the person sounded like your boss, your colleague, or your family member, that social signal carried weight.
AI makes that obsolete. The marginal cost of impersonation is falling. A short audio sample can be enough to generate a convincing clone in many contexts [6][7]. That turns “urgent wire transfer” scams, family emergency scams, and executive impersonation from rare and bespoke events into repeatable playbooks.
The risk is not only the clone. It is the time pressure. Many voice scams work because they compress a decision into seconds. The caller is “in a meeting,” “boarding a flight,” or “handling a crisis.” If the voice sounds right, people bypass normal checks.
This is why security guidance increasingly treats voice and video as unreliable signals [6][7]. Familiarity is no longer proof.
| Question | Before | With voice cloning |
|---|---|---|
| What a familiar voice proves | It worked as informal authentication: never perfect, but the social signal carried weight | Nothing on its own: security guidance increasingly treats voice and video as unreliable signals (FBI Internet Crime Complaint Center (IC3)) |
| What impersonation scams look like | Rare and bespoke events | Repeatable playbooks for urgent wire transfers, family emergencies, and executive impersonation, as the marginal cost falls and a short audio sample can be enough in many contexts (Federal Trade Commission, Consumer Advice) |
3) Recon and social engineering scale up
Spear-phishing used to be high-effort because the recon was high-effort. Attackers needed time to map an organization, identify targets, and craft a believable pretext. That cost filtered targets. Smaller firms were often not worth it.
AI changes the economics. It can help generate basic org charts, draft plausible pretexts, and produce target-specific scripts. It can summarize a company’s public footprint and propose angles that match the target’s role. This does not mean attackers automatically get perfect intel. It means the baseline cost of trying is lower.
That matters for small and mid-sized organizations. When tailored social engineering becomes cheap, “we are too small to be targeted” stops being a strategy.
4) Malware gets more adaptive, even when the core exploits are not new
Polymorphic malware existed before AI [8]. So did skilled attackers who could iterate quickly. The shift is that certain parts of the attacker workflow become more accessible and faster. Drafting scripts, generating variants, creating lures, and adapting payload delivery can be accelerated, even if sophisticated operations still require expertise.
This compresses the attack loop. Generate a variant. Test it against defenses. Adjust and resend. Defenders have to be correct every day. Attackers only have to be correct once. When iteration gets cheaper, the once becomes easier to find.
Old phishing vs. AI-enabled phishing
| Pattern | Pre-AI phishing (common) | AI-enabled phishing (first-wave pattern) |
|---|---|---|
| Message quality | Sloppy language and obvious red flags | Fluent, plausible tone and fewer obvious tells |
| Targeting | Broad blasts | Light recon + tailored pretext at low cost |
| Iteration | Slow, manual crafting | Fast variant testing and refinement |
| Failure mode | Humans spot “this looks fake” | Humans miss it. Controls have to catch it |
Voice-clone scam flow and the verification ladder
Text version
- Urgent request: (pressure + authority)
- Voice match triggers trust: “it sounds like them”
- Normal checks bypassed: exception path
- High-risk action: wire transfer, vendor change, MFA reset
- Loss discovered later: after funds move or access persists
Text version
- Low risk requests: normal workflow
- Medium risk: MFA + role-based controls
- High risk: out-of-band verification + dual approval + limits
What this means for defense (the posture shift)
The correct mindset is not “we will block everything.” It is a posture built around three assumptions. First, some attacks get through. Second, the objective is to reduce blast radius. Third, high-risk actions should be hard to authorize even when someone is persuaded.
This shifts attention away from only perimeter defenses and toward system design. Least privilege matters because it limits what a compromised account can do. Strong multi-factor authentication matters, but it should not rely on voice or video. Out-of-band verification matters for money movement and sensitive access because it forces a second channel that an attacker cannot easily spoof at the same moment. Rapid detection and containment matter because speed often beats perfection.
Visual: Attack funnel
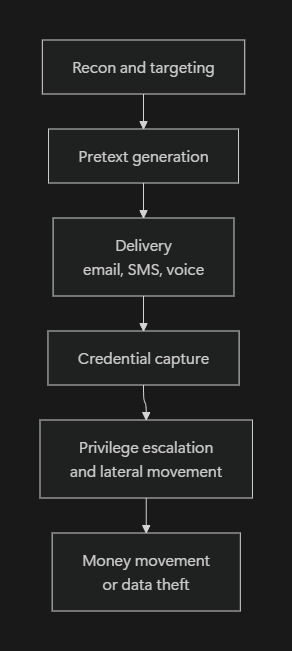
Practically, this means investing in boring controls that hold up under persuasion. It means documenting how money moves and making exceptions rare. It means limiting who can change payment instructions, who can create new vendors, and who can approve urgent transfers. It also means treating “urgent requests” as a risk pattern rather than as a reason to waive process.
A simple takeaway
AI is not creating new human weaknesses. It is industrializing the old ones. For the next few years, that industrialization favors attackers.
The defense response is not panic. It is governance. Assume compromise. Reduce blast radius. Make the most expensive mistakes harder to make.
Sources
- UK National Cyber Security Centre (NCSC), The near-term impact of AI on the cyber threat (AI likely increases scale and sophistication in the near term): https://www.ncsc.gov.uk/report/impact-of-ai-on-cyber-threat
- Verizon, Data Breach Investigations Report (DBIR) (phishing and social engineering prevalence): https://www.verizon.com/business/resources/reports/dbir/
- FBI, Internet Crime Report (IC3) (fraud and BEC context): https://www.ic3.gov/
- CISA, phishing guidance (controls and defensive posture): https://www.cisa.gov/resources-tools/resources/phishing-guidance-stopping-attack-cycle-phase-one
- NIST, AI Risk Management Framework (AI RMF 1.0) (risk framing and governance posture): https://www.nist.gov/itl/ai-risk-management-framework
Additional reading
The Rational Moderate
- AI Regulation Turns Real: The First Wave of State Laws Takes Effect
- What “algorithmic transparency” really means
External
- NCSC, near-term AI cyber threat: https://www.ncsc.gov.uk/report/impact-of-ai-on-cyber-threat
- Verizon DBIR: https://www.verizon.com/business/resources/reports/dbir/
- FBI IC3: https://www.ic3.gov/